W
01 · featurediOS
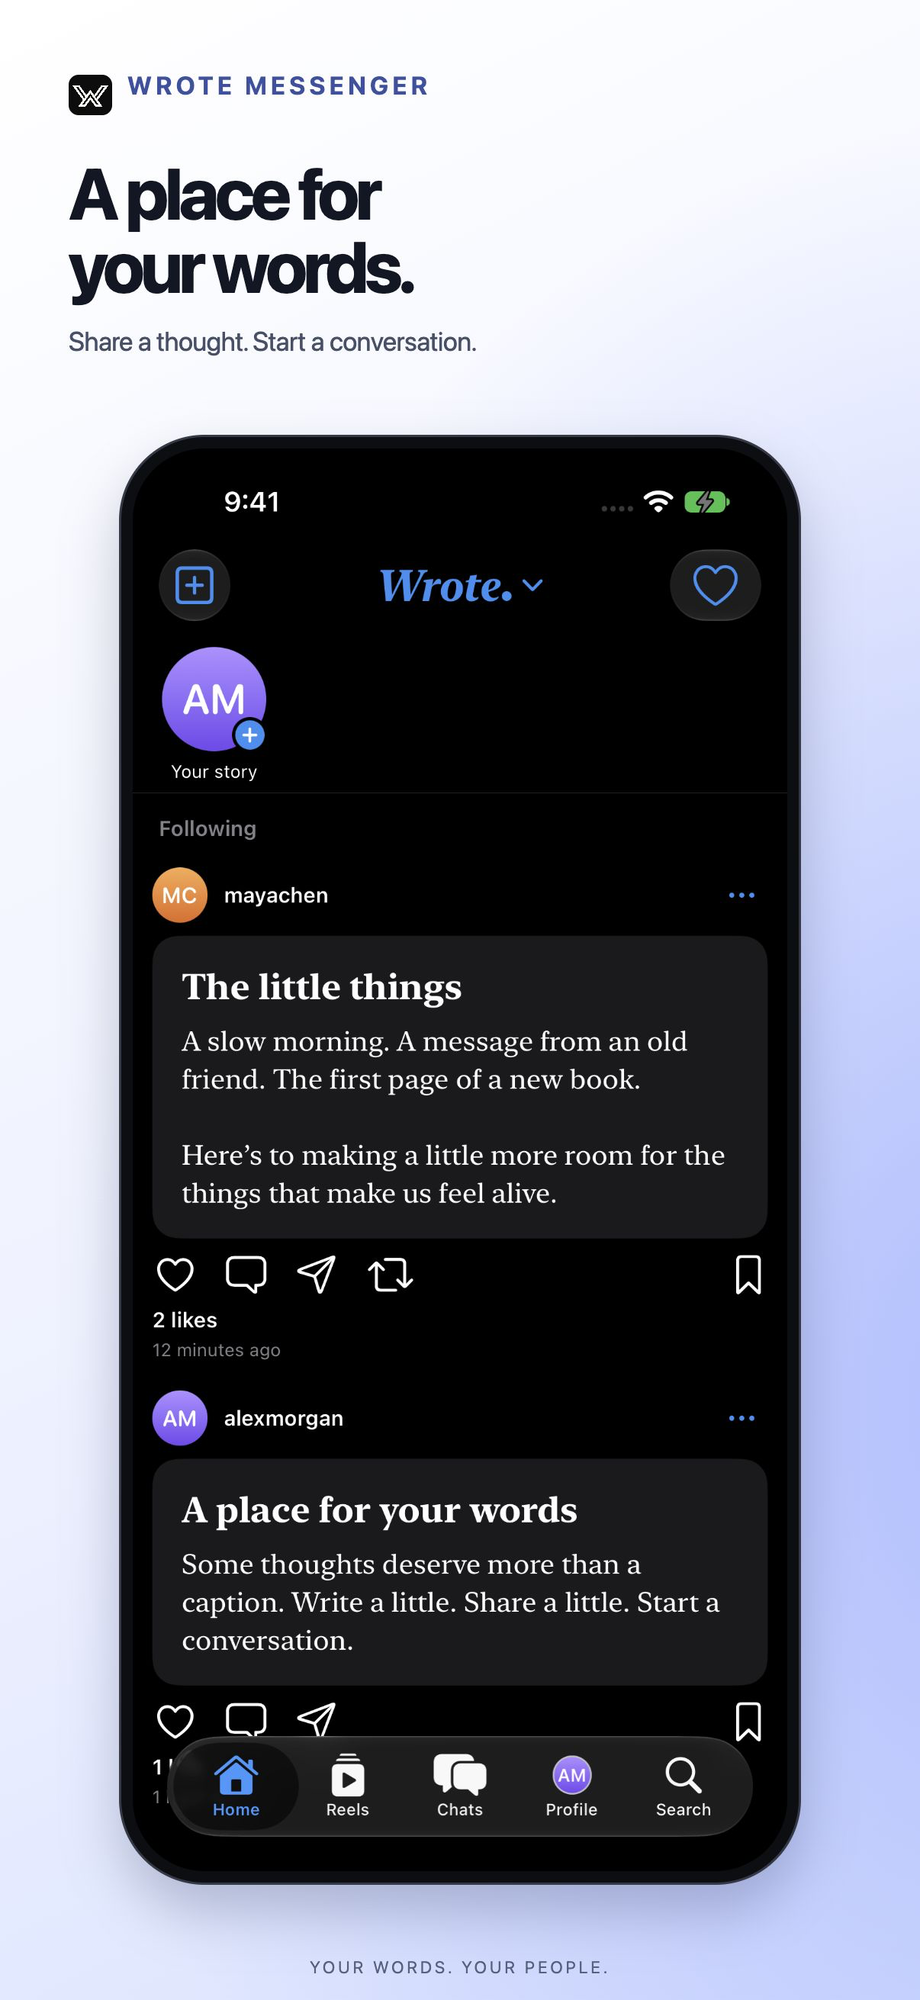
Wrote Messenger
A social messaging experience founded on 16.07.2027, originally on wt.mk and now on wrote.sh.
Developer / builder / curious mind.
A social messaging experience founded on 16.07.2027, originally on wt.mk and now on wrote.sh.
A Roblox UGC store creating 3D accessory items, development services, scripts, software, and commissions.
Visit Formale ↗
A Discord moderation and community-security platform centered on a verified Global Ban Database.
Safe-Guard.gg was founded in 2023 and actively developed throughout 2024. Its dashboard managed bot configurations, moderation records, and integrations with Discord servers, FiveM server scripts, and Roblox experiences. Reports were reviewed by staff before validated information entered the Global Ban Database, helping participating communities identify and restrict verified bad actors. The project was officially discontinued near the end of 2024.
Started with Discord bots, then expanded into Java and building more complete applications.
Scripts and utilities for monitoring, automation, and changing how applications behave.
Early experiments, random websites, Roblox experiences, and FiveM server projects.
My first official backend language, used for Safe-guard.gg and forum and pastebin projects.
App development that began at 18 and continued into 19 with a focus on iOS.
Roblox experiences focused on systems rather than visual design, including troubleshooting, fixes, security patches, anti-exploitation work, and creating new game systems.
I’m currently working toward a couple of cybersecurity certificates. They’ll be added here once the coursework and exams are complete.
I enjoy investigating individuals, organizations, and incidents through OSINT and CSINT research, public records, and databases where access is authorized. I’m not currently a licensed private investigator, but may pursue licensure in the future.
I recently started exploring vulnerability research, penetration testing, and responsible bug-bounty programs. I use Linux virtual machines and VPS environments, switching between Kali Linux and Parrot Security OS for authorized testing.
Worked in IT Support across Green State Hosting and its later Hamz Hosting transition, responding to support tickets, resolving hosting issues, and helping keep customer servers and services running reliably.
Retired from Hamz Hosting before it transitioned to a different company name, ownership, and management. Worked closely with Patty Curtis (PattysDevelopment) and other teams to diagnose and fix server issues.
Helped build the first version of Loki.lol, a biolink service, working alongside its founder, known online as Xoru. Contributed to both the frontend and backend as the service grew from its initial launch into a more established platform.
The service gained wider attention during the early build period and was sold a few months later under new ownership.
Have a question, idea, or opportunity? Email me and I’ll respond within 24–72 hours.